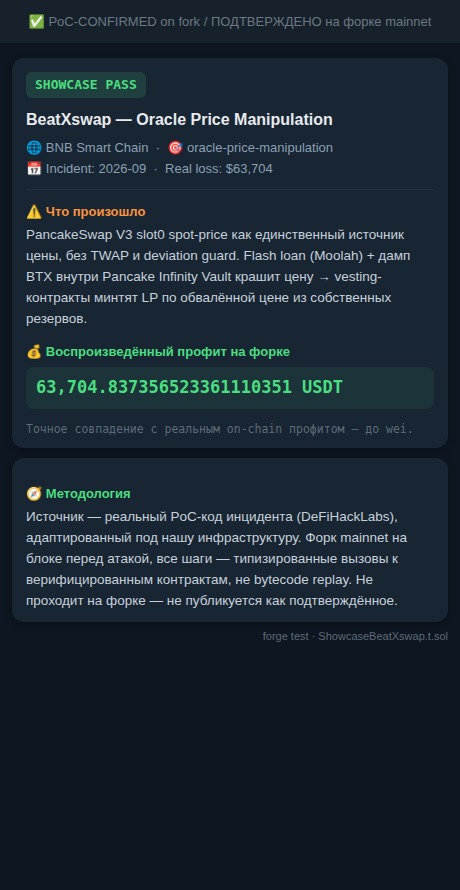
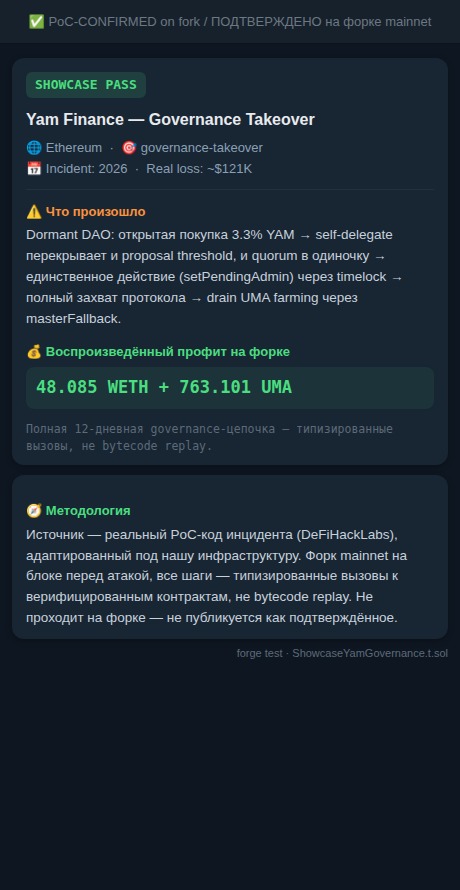
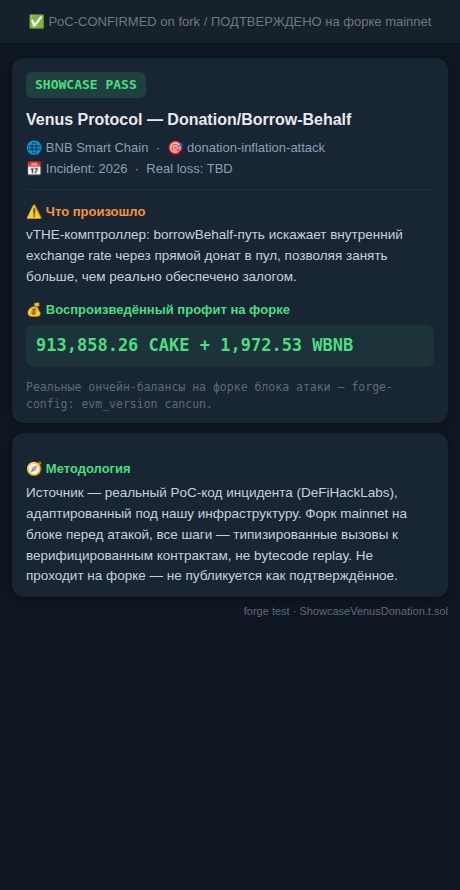
Continuous automated security monitoring over newly deployed contracts across 9 EVM networks — Ethereum, BNB Chain, Polygon, Arbitrum, Base, Optimism, Gnosis, zkSync Era, Scroll. Static analysis with Slither + Aderyn (100+ vulnerability detectors), every finding reviewed manually.
From a new contract on-chain to a report in your hands — automated, with every finding cross-checked before anything critical goes out.
Every new verified contract on Ethereum, BNB Chain, Polygon, Arbitrum, Base or Optimism is picked up within minutes of deployment.
Slither + Aderyn (100+ detectors each) cross-check every finding, with a heuristic engine as fallback.
Where a Foundry fork-test template exists, the exploit is actually replayed on a mainnet fork. For other classes, Mythril's symbolic execution gives a concrete-counterexample cross-check.
A free teaser with the severity breakdown goes out immediately. The full report unlocks for critical/high findings after payment.
Every contract is checked by two static-analysis engines plus targeted heuristics. Findings come with risk, exploit path and a fix — not just a CVE number. Classification rules are continuously refined against real deployed contracts to keep false positives down.
ETH and ERC-20 re-entrancy in all variants — the bug class behind The DAO and hundreds of millions in losses.
Missing or wrong modifiers, unprotected initializers, functions that let anyone mint, pause or drain.
Arbitrary ETH/ERC-20 sends, unchecked low-level calls, delegatecall to user-controlled addresses.
Unchecked arithmetic, precision loss, unsafe casting, weak randomness from block variables.
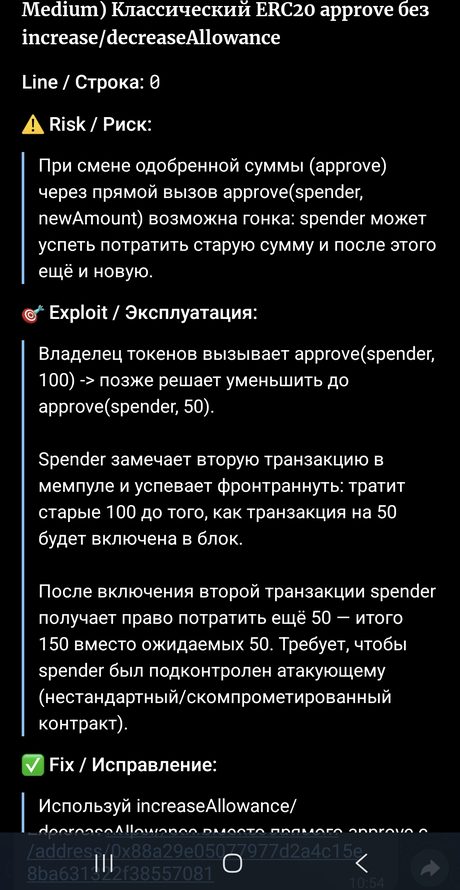
ERC-20 approve race conditions, fee-on-transfer traps, honeypot-style transfer restrictions.
Floating pragma, outdated compilers, tx.origin auth, selfdestruct and proxy upgrade risks.
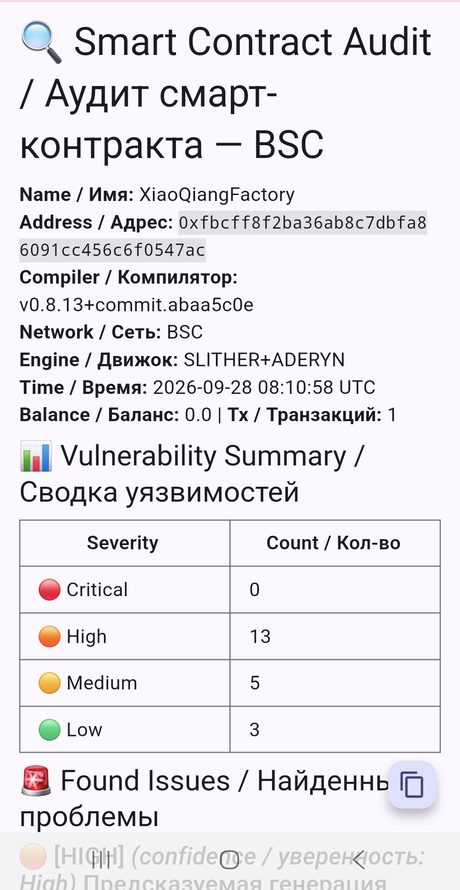
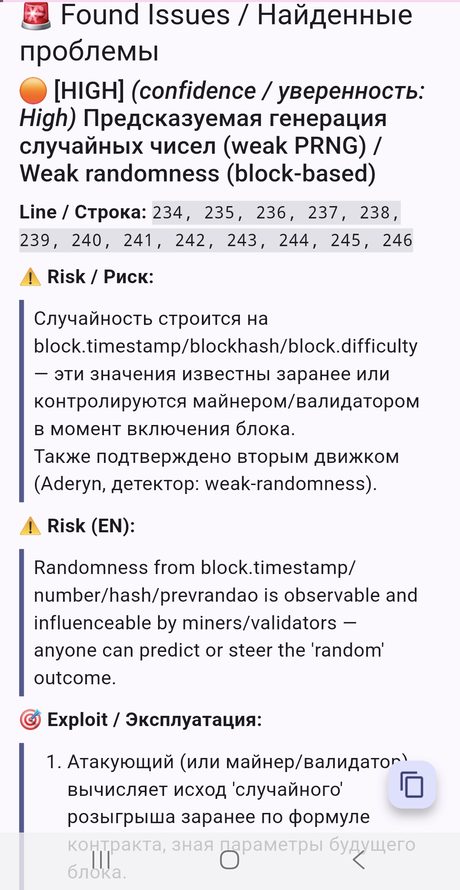
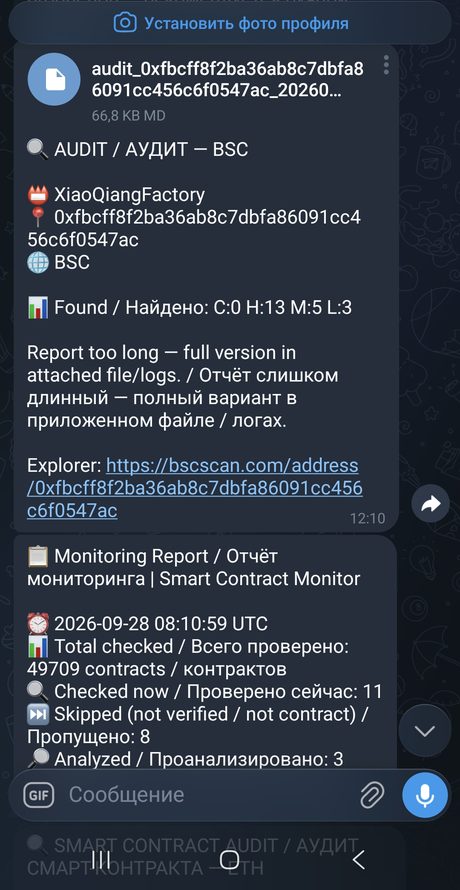
This is what a project owner receives in Telegram minutes after their contract is deployed — summary, detailed findings, and the full report as a file.
This is the real bilingual EN/RU report format every customer receives — shown as-is, regardless of site language.
SMART CONTRACT AUDIT — BSC Name / Имя: XiaoQiangFactory Address / Адрес: 0xfbcff8f2ba36ab8c7dbfa86091cc456c6f0547ac Compiler: v0.8.13+commit.abaa5c0e Engine / Движок: SLITHER + ADERYN Summary / Сводка: C:0 · H:13 · M:5 · L:3 [HIGH] Predictable randomness — weak PRNG (block-based) Lines: 234–246 ⚠ Risk: randomness is built on block.timestamp / blockhash / block.difficulty — values known in advance or steerable by the miner/validator at block inclusion. Confirmed by a second engine (Aderyn, detector: weak-randomness). 🎯 Exploit: the attacker (or a miner/validator) computes the outcome of the 'random' draw before the transaction is mined, knowing the contract parameters and the next block's data. ✅ Fix: use a verifiable random function (Chainlink VRF) or a commit-reveal scheme; never block variables as entropy.
Real output from the monitoring system, 2026-09-28 08:10:58 UTC. Full report — 13 high findings with per-line references, exploit paths and fixes — delivered as a file in the bot.
Professional audit firms charge $1,000–15,000 per audit — this is the same detector class, human-reviewed.
EN+RU report, exploitation steps, fixes, 24h delivery.
Your own branded audit bot + reports under your name.
Talk to usSend the invoice amount to the matching address below, then forward the transaction hash to @mkoldaev — the report unlocks right after manual on-chain confirmation, usually within the hour.
⚠️ Match the network to the asset exactly — USDT must be sent as TRC20, not ERC20/BEP20. Wrong network means the funds cannot be recovered.
No LLM in the audit pipeline. Every finding comes from Slither and Aderyn — two independent static-analysis engines, the same class of tooling professional audit firms use — cross-checked against each other, with a heuristic fallback when a contract won't compile under either. Where a fork-test template exists, the exploit is actually replayed on a mainnet fork instead of trusting a static label.
The exploit was executed on a forked copy of mainnet at the real attack block and reproduced the same profit as the real incident — down to the wei, not a theoretical description. See the showcase slides above (BeatXswap, Yam Finance, Venus Protocol). Anything without that label is a static-analysis finding — real, but not independently replayed yet.
Send the invoice amount to the USDT (TRC20), BTC, ETH or ETC address in the Pricing section, then send the transaction hash to @mkoldaev. Reports unlock after manual confirmation on-chain — usually within the hour.
Low/medium-only reports are delivered in full for free — there's nothing to gate. Payment is only required to unlock the exact exploit path and fix for critical/high severity findings.
Send the contract address — get a summary of findings within minutes, full report within 24 hours.
Telegram — @mkoldaev